and extracts the following text as a script body — the dev server then fails its dependency scan with `Expected ";" but found "non"` from the words "non-allowlisted hosts", which breaks e2e. So, what this buys, so nobody reads more or less into it: blocks external `script src=` from non-allowlisted hosts blocks injected inline scripts — each one is pinned by hash blocks fetch/XHR/WebSocket exfiltration (connect-src allowlist) blocks form-action, base-uri, object-src vectors does not stop image-based exfiltration — img-src must allow https: because event media comes from arbitrary publishers' og:image The cost of hashing is that an inline script edited after the hashes are computed is silently refused by the browser. That is why the violation reporter below exists: report-uri/report-to are ignored in a meta element and Pages serves no CSP header, so violations are caught in-page and sent to PostHog instead (src/lib/csp-report.ts, #241). frame-ancestors is deliberately NOT in this string: it is ignored in a meta element and browsers log a warning about it on every page load. It lives in public/_headers instead, ready for a CDN in front of Pages. X-Frame-Options (set there too) is the clickjacking control that actually applies today. */ }
update

Kenya Confirms Second Ebola Case, a Quarantined Relative of the First

| Ebola

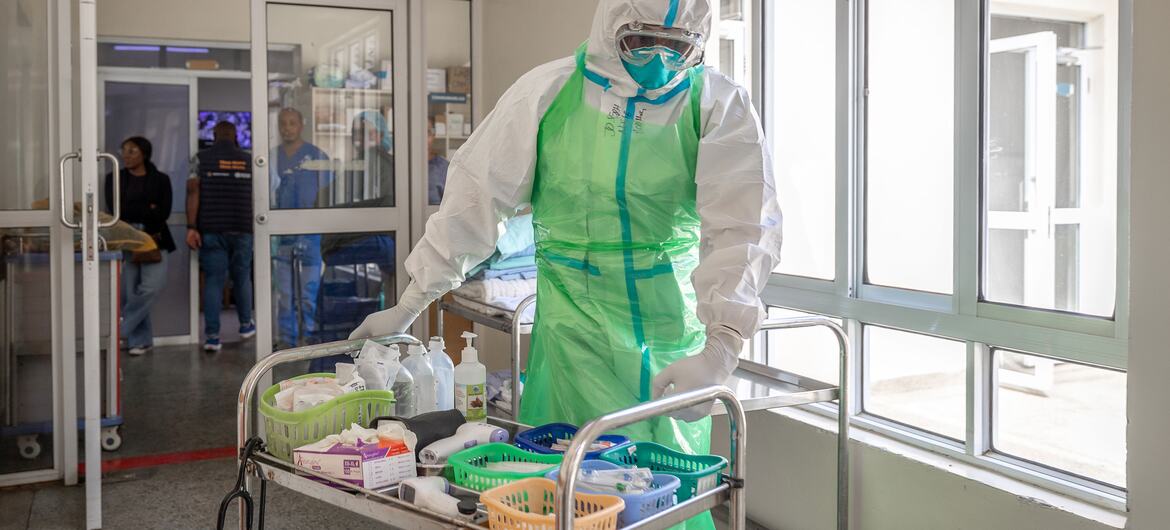
WHO is supporting Kenya after a 39-year-old man, a relative of the first patient, tested positive for Bundibugyo virus. He was already in quarantine as a contact and developed symptoms on 13 October. The first case arrived in Nairobi via Uganda on 3 October and died two days later. More than 40 contacts have been identified; WHO says no community spread has been detected and does not recommend travel restrictions.

WHO supports Kenya's Ebola response
WHO supports Kenya's Ebola response — UN News